Serbay Çetinkaya, Anomaly Detection in DNS Over HTTPS Traffic Using An Autoencoder Based Approach
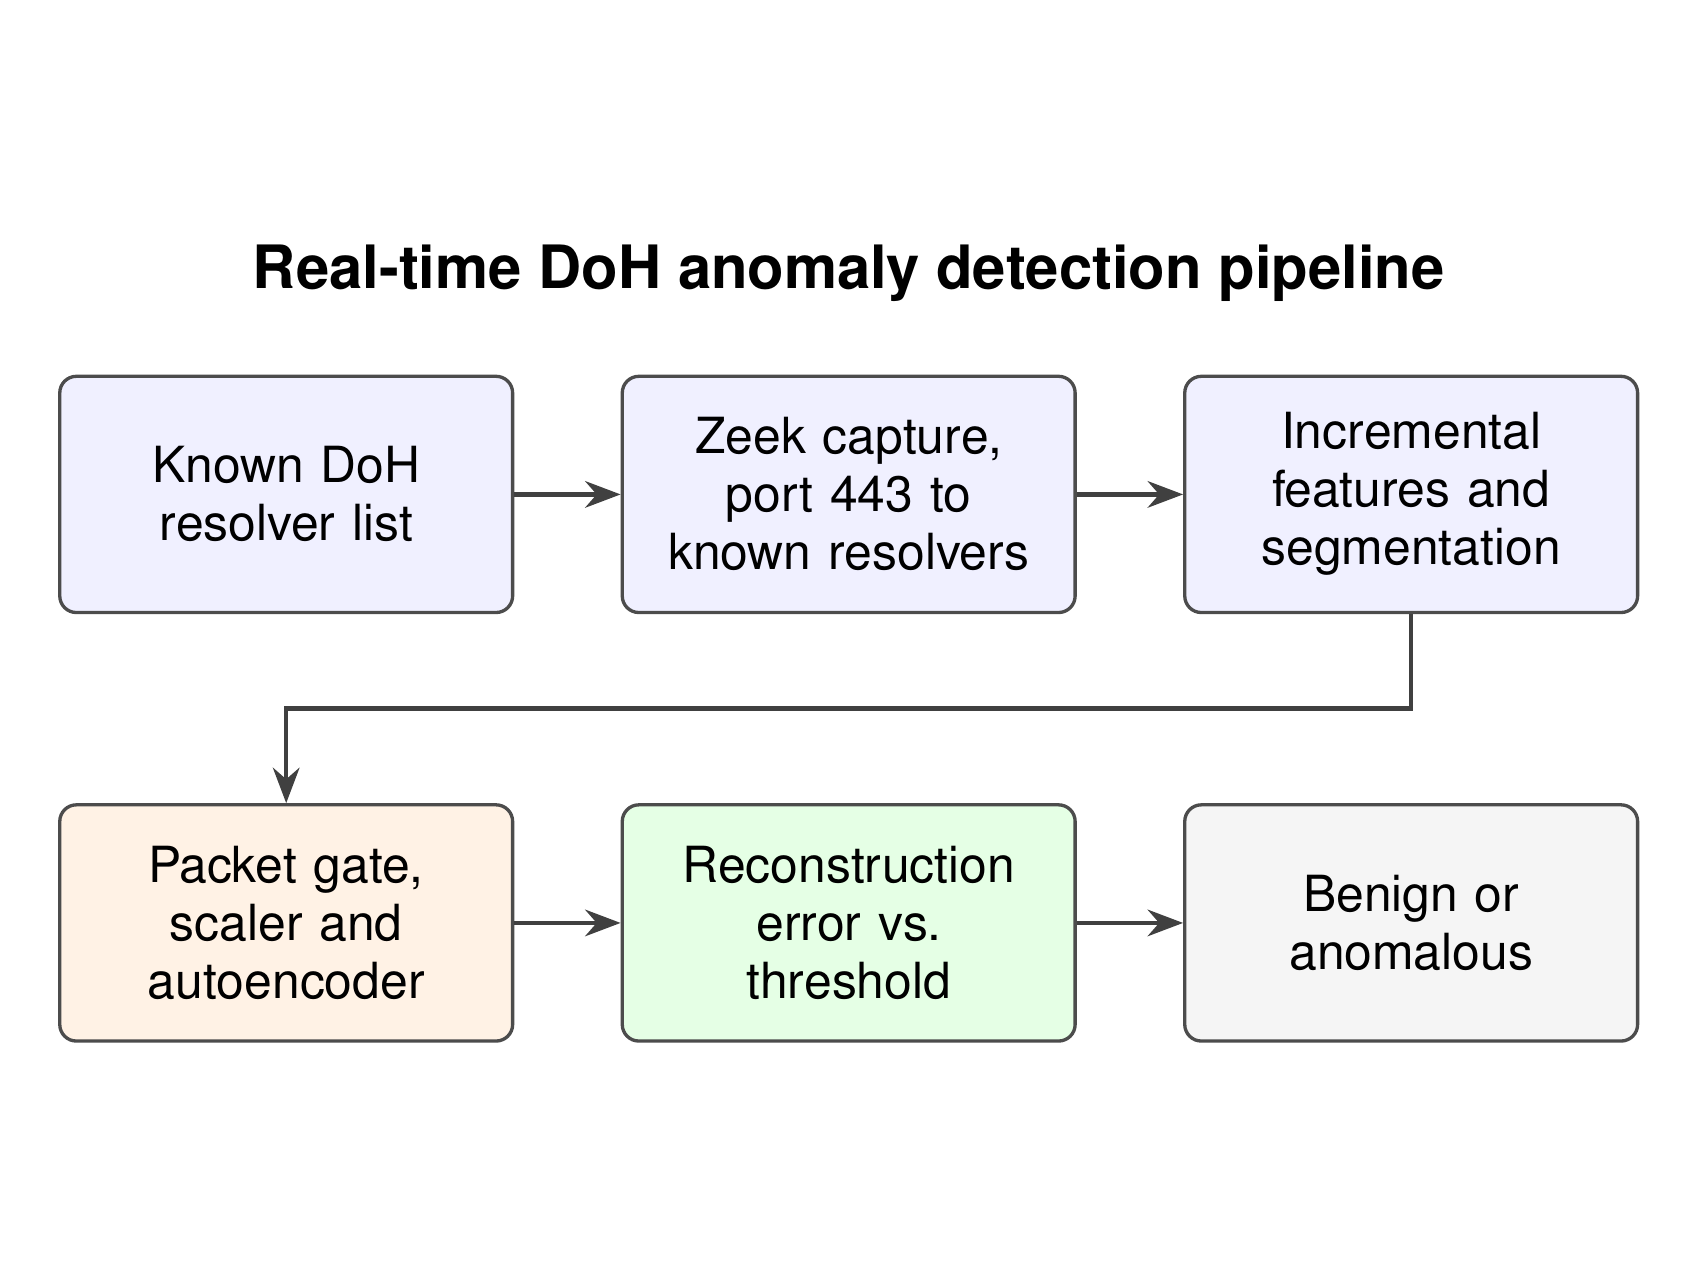
Encrypted DNS protocols such as DNS over HTTPS (DoH) protect user privacy, but attackers can use them to hide malicious activity such as data exfiltration and command and control traffic. This thesis proposes an autoencoder based approach that learns only from benign DoH traffic and flags flows with high reconstruction error as anomalies. To enable real-time detection, the model uses sixteen flow features that can be computed while a connection is active, and a Zeek based pipeline extracts them from live traffic. On the BCCC-CIRA-CIC-DoHBrw-2020 dataset, the model detected 99% of malicious flows with an overall accuracy of 0.945.
Date: 13.11.2026 / 11:00 Place: B-116
English